
Key Takeaways
- The OpenClaw playbook assembles a working executive ops agent in four to six hours, cutting inbox triage time by 60 to 70 percent while keeping human approval on every outbound message.
- Drafting is separated from sending at the infrastructure level: OAuth scopes exclude the send scope, so dangerous actions are unavailable to the model rather than merely discouraged by prompts.
- Governance, not scheduling, is the real blocker — no default spending cap, unverified skill risk, and 22 percent of surveyed employees running OpenClaw without IT approval.
Table of Contents
The Four-Hour Executive Ops Agent Stack
n8n Lab reports that operations teams can now assemble an OpenClaw agent stack in four to six hours that triages executive inboxes, checks calendar availability, drafts replies, and extracts tasks without ever sending a message unattended.
The playbook targets executive assistants and operations coordinators who currently spend hours cross-referencing calendars, enforcing buffer times, drafting context-aware replies, and tracking follow-ups.
By moving those functions into a scheduled or trigger-based pipeline, teams can reduce inbox triage time by 60 to 70 percent while preserving a mandatory human-in-the-loop approval layer for every outbound communication.
Inside the OpenClaw Calendar, Email, and Task Pipeline
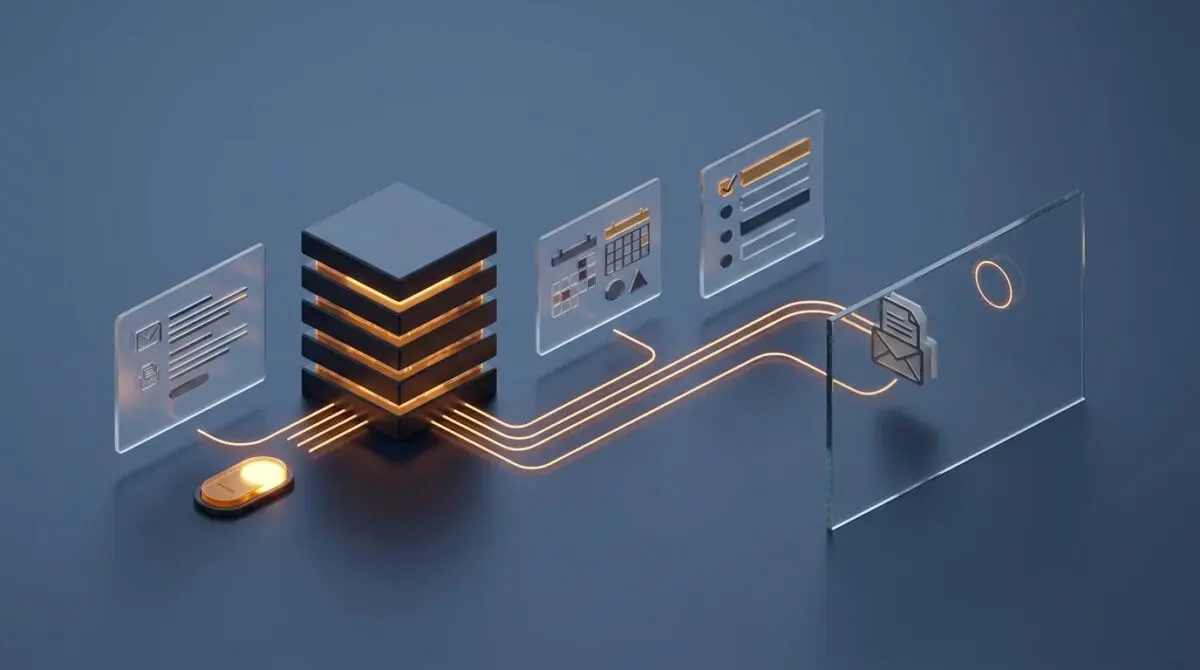
The reference architecture in n8n Lab’s playbook isolates permissions so the agent reads data, formulates a plan, executes read operations to gather context, and executes limited write operations to stage drafts.
The build uses OpenClaw as the agent framework, Node.js MCP servers for tool connectivity, Google Workspace API or Microsoft Graph API for calendar and email access, and Claude 3.5 Sonnet for reasoning.
Claude 3.5 Sonnet handles intent detection, VIP sender recognition, meeting-time extraction, and tool selection, while the MCP servers manage the rigid math and API-specific logic.
Five-Layer Control Loop
The architecture follows a five-layer agent framework that separates triggers, reasoning, tools, memory, and guardrails.
- Trigger — a cron schedule runs every 15 minutes or an assistant launches it manually through OpenClaw.
- Reasoning — Claude 3.5 Sonnet analyzes email intent, extracts requested meeting times, flags VIP senders, and decides which tools to call.
- Tools — MCP servers expose email fetching, draft creation, calendar availability checks, event creation, and task logging.
- Memory — a static markdown file stores working hours, VIP contacts, buffer times, and response tone preferences.
- Guardrails — the email tool only creates drafts, the calendar tool creates tentative holds, and unrecognized intents escalate to the assistant.
The strongest design choice is the separation of drafting from sending at the infrastructure level.
The playbook instructs teams to request only read and draft scopes when generating OAuth credentials, explicitly excluding the ‘send scope’.
This makes a dangerous outbound action unavailable to the model rather than relying solely on prompt instructions.
Email, Calendar, and Task Tool Schemas
The email layer defines two core tools: one fetches unread messages and one creates draft replies within the original thread.
The calendar layer exposes a free-slot search tool and an event creation tool, pushing buffer-time math into server code rather than leaving it to the model.
For task extraction, an action-item tool connects to Notion or Linear and creates concise tasks with direct links back to the source email thread.
Escalation is the final guardrail: sensitive topics or ambiguous requests are routed through a dedicated tool that logs the email into a high-priority channel or task list.
When a VIP requests a time already occupied by a lower-priority internal meeting, the agent drafts a reschedule request to the lower-priority participant and an acceptance to the VIP, then flags all three actions for assistant review.
It never deletes the existing internal meeting on its own.
The core configuration lives in a skill definition file that points to system prompts and MCP server binaries, with API keys supplied through environment variables rather than committed to version control.
Before connecting a live executive inbox, the playbook requires verifying tool calls in a sandbox, limiting OAuth scopes to read and draft permissions, and setting up webhooks for crash or rate-limit alerts.
A final autonomy test deliberately commands the agent to send an email, verifying that the operation fails because the tool does not exist.
Guardrails, Cost Pressure, and the Security Friction Point
The technical pattern is sound, but the strategic picture is more contested once OpenClaw moves into production environments.
OpenClaw functions as an always-on agent runtime built around an observe, reason, act, and persist loop, with a gateway control plane handling routing, access control, and session persistence.
The 2.0 release adds restart-safe automation: interrupted runs resume without redoing completed work, accepted messages persist through reconnects, and approvals stay bound to the exact request, command, session, and person.
Security controls in that release are materially stronger: credentials never pass through model-visible text, stale authority is rechecked before an action runs, and removing or re-pairing a device retires old access.
Still, community security threads continue to describe prompt-injection risks, particularly for agents with access to email, logins, or financial accounts, and several practitioners say human-in-the-loop approvals and sandboxing reduce but do not eliminate that exposure.
Those are not formal audit findings, but they are consistent with the playbook’s own insistence that the agent must never be allowed to send unattended or hard-delete calendar events without human approval.
A vendor-authored competitive comparison raises sharper governance concerns: OpenClaw has no built-in spending cap by default, and every message, decision, or action can trigger billable API usage.
The same comparison cites a Bitdefender finding that roughly 20 percent of ClawHub skills may be malicious, and a Token Security survey showing 22 percent of customers have employees running OpenClaw without IT approval.
Those figures are vendor-selected and have not been independently verified in formal production benchmarks, but they underscore a real governance gap for automation teams.
Hosting guidance from commercial providers suggests 4 GB of RAM as the functional minimum for a production OpenClaw process, with heavier browser automation or local models requiring more.
Promotional pricing for a 4 GB NVMe plan can start as low as $9.49 per month on a 24-month term, though that is vendor marketing rather than an independent infrastructure recommendation.
On the API side, the playbook estimates processing 100 emails per day with Claude 3.5 Sonnet typically costs between $2 and $5 daily, with batching and model routing as the main cost controls.
Batching up to 50 unread emails into a single reasoning step and routing only scheduling-related messages to Claude 3.5 Sonnet can significantly reduce token consumption.
The risk of silent cost spikes is not hypothetical: a brief Anthropic subscription-billing change earlier in 2026 pushed some users’ bills up as much as 50 times overnight before being reversed.
For managed interoperability, OpenClaw supports MCP and can connect to larger automation platforms through their MCP servers, but that does not automatically secure OpenClaw’s own runtime, skills, or system-level access.
Enterprise Anthropic or OpenAI API tiers can prevent training on executive inbox data, but the raw message content still leaves the network for inference, so compliance review remains a precondition for deployment.
Multi-executive deployments require separate agent instances or threads because a shared memory file will cross-contaminate scheduling logic and calendars.
Automation leaders should treat this as a governance problem first and a scheduling problem second.
What Automation Teams Must Decide Now
The OpenClaw executive assistant pattern works because it treats human judgment as the final execution layer, but the real decision for automation teams is whether their governance, cost controls, and runtime isolation are strong enough to deploy it beyond a test inbox. For teams building executive assistant agents that need to scale safely, programmatic SEO and AI automation engineering is how Andres SEO Expert approaches the same human-in-the-loop discipline — start the conversation here.
Frequently Asked Questions
What is the OpenClaw executive ops agent stack?
The OpenClaw executive ops agent stack is a reference architecture that uses OpenClaw, Node.js MCP servers, Google Workspace or Microsoft Graph APIs, and Claude 3.5 Sonnet to triage executive inboxes, check calendar availability, draft replies, extract tasks, and escalate sensitive items. It is designed for executive assistants and operations coordinators who need automation without unattended outbound communication.
How long does it take to build an OpenClaw executive assistant agent?
n8n Lab reports operations teams can assemble it in four to six hours. The build includes OAuth setup, MCP tool schemas, a memory file, guardrails, and sandbox testing before connecting a live executive inbox.
How does OpenClaw keep email sending human-in-the-loop?
The agent only has read and draft OAuth scopes, explicitly excluding send scope. The email tool can create drafts but cannot send. The calendar tool creates tentative holds, not confirmed events. Sensitive or ambiguous requests escalate to a human. A final autonomy test tries to send an email and verifies the operation fails because the tool does not exist.
What are the five layers of the OpenClaw agent control loop?
The five layers are trigger, reasoning, tools, memory, and guardrails. Trigger is a cron schedule every 15 minutes or a manual launch. Reasoning uses Claude 3.5 Sonnet for intent detection, VIP recognition, meeting-time extraction, and tool selection. Tools are MCP servers for email fetching, draft creation, calendar availability, event creation, and task logging. Memory is a static markdown file for working hours, VIP contacts, buffer times, and tone. Guardrails restrict email to drafts, calendar to tentative holds, and unrecognized intents to escalation.
How much does it cost to run an OpenClaw executive assistant per day?
The playbook estimates processing 100 emails per day with Claude 3.5 Sonnet typically costs between $2 and $5 daily. Batching up to 50 unread emails into one reasoning step and routing only scheduling-related messages to Claude 3.5 Sonnet are the main cost controls. OpenClaw has no built-in spending cap by default, so cost governance is required.
What security risks remain with OpenClaw email and calendar agents?
Community security threads describe prompt-injection risks, especially for agents with access to email, logins, or financial accounts. Human-in-the-loop approvals and sandboxing reduce but do not eliminate that exposure. A vendor comparison cites a Bitdefender finding that roughly 20 percent of ClawHub skills may be malicious, and a Token Security survey showing 22 percent of customers have employees running OpenClaw without IT approval. Those figures are vendor-selected and have not been independently verified.
Can one OpenClaw agent support multiple executives?
No. Multi-executive deployments require separate agent instances or threads because a shared memory file will cross-contaminate scheduling logic and calendars. Each executive should have isolated working hours, VIP lists, buffer times, and calendar permissions.