
Key Takeaways
- Cloudflare CASB policies turn passive findings into event-driven action, revoking public file shares or firing webhooks in five minutes or less.
- The remediation engine runs on Queues, Workers, and Workflows, making durable execution, automatic retries, and rate-limit backoff the baseline for production automation.
- Dual logs in Cloudflare One Insights capture admin changes and runtime outcomes, creating a proof-of-fix audit trail for compliance teams.
Table of Contents
CASB Policies Turn Passive SaaS Alerts Into Self-Healing Workflows
A misconfigured public file share can now be revoked before a security analyst finishes reading the alert.
Cloudflare has rolled out automatic remediation policies inside its Cloud Access Security Broker, moving SaaS security findings from a passive backlog to event-driven execution.
Security teams can now define response logic once: revoke risky file shares, dispatch webhooks to a SOC, or trigger both actions the moment a finding appears.
The change targets a long-standing gap in SaaS Security Posture Management: most tools identify exposure but leave the fix to overworked administrators.
Inside the Event-Driven Remediation Engine Behind CASB Policies
Cloudflare CASB already surfaced risks like overshared files, dormant admin keys and tokens, and OAuth apps with excessive permissions.
Its new CASB policies are a native automation engine built directly into Cloudflare One.
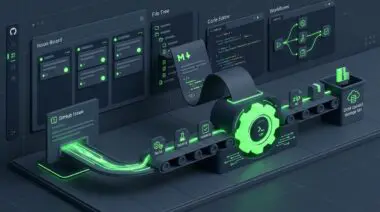
When a finding is detected, the findings engine enqueues an orchestration message to a Cloudflare Queue.
A Worker consumer checks whether the incoming finding matches a policy configuration and creates a corresponding job.
That job passes to a remediation pipeline running on Cloudflare Workflows, which provides durable and fault-tolerant execution.
Process restarts and retries are handled automatically.
Third-party API rate limits are managed with backoff windows, so a vendor’s throttling response does not cause a dropped task.
The stated performance target from detection to completed remediation is five minutes or less.
Policies can include a remediation action, a webhook action, or both.
Admins select a vendor, integration or tenant, finding type, and action when creating a policy.
First-party remediation currently supports Microsoft and Google Workspace file and folder findings, while webhook destinations include Slack, Microsoft Teams, Jira, ServiceNow, Tines, or any custom HTTP endpoint.
A practical example involves public file sharing policies.
Organizations may prohibit public shares while allowing exceptions for marketing teams that collaborate externally.
Instead of queuing every violation for manual review, a CASB policy can revoke public access immediately when a share falls outside the approved exception.
That keeps the finding backlog clean and minimizes the exposure window.
Each policy action also produces two categories of logs under Cloudflare One Insights.
- Admin Activity logs. Track who created, edited, or disabled a policy.
- Cloud & SaaS Security policies logs. Capture runtime outcomes, including which finding triggered the policy, which file was acted on, and whether execution succeeded or failed.
The execution log functions as a proof of fix, tying a specific finding to a specific automated action and timestamp.
The Five-Minute Bar for SaaS Security Automation
For automation engineers, the most consequential part of this release is architectural, not just security focused.
The policy engine is built on the same developer platform available to every customer: Queues, Workers, and Workflows.
That means durable execution, automatic retries, and rate-limit backoff are becoming baseline expectations for any production automation pipeline.
Event-driven remediation also shifts the role of the SOC from continuous manual triage to policy design and exception handling.
Instead of reviewing hundreds of similar public share findings, operators can encode the intended boundary once and let the engine enforce it.
For compliance teams, the runtime log is a stronger audit artifact than a stale checkbox.
It records the finding, the asset, the action, and the result, which is what regulators and internal auditors increasingly expect.
The upcoming support for custom findings should expand automation beyond default risk taxonomies.
That will allow organizations to attach automated actions to business-specific detection logic rather than relying solely on vendor-defined risks.
For teams still running manual remediation backlogs, the five-minute target offers a concrete benchmark to measure internal response workflows against.
That target is particularly meaningful for sensitive files such as financial reports, legal documents, or intellectual property, where hours of exposure can translate into real damage.
Why Automation Practitioners Should Watch CASB Policies
CASB policies move SaaS security automation from a human-powered response loop to a configured, event-based enforcement loop. For teams still clearing manual backlogs of overshared files, that shift is immediate. For teams building event-driven remediation pipelines and cloud security automations that need to scale, programmatic SEO and AI automation is how Andres SEO Expert approaches technical content and automation strategy — get in touch.
Frequently Asked Questions
What are Cloudflare CASB policies?
Cloudflare CASB policies are native automation rules inside Cloudflare One that turn SaaS security findings into event-driven remediation workflows. They let admins define response logic once and apply it automatically when a matching finding appears.
How do Cloudflare CASB policies automate remediation?
The findings engine enqueues an orchestration message to a Cloudflare Queue. A Worker consumer matches the finding to a policy and creates a job. Cloudflare Workflows then runs the remediation pipeline with durable execution, automatic retries, and rate-limit backoff.
What actions can a CASB policy perform?
A policy can run a first-party remediation action, send a webhook, or both. Examples include revoking risky file shares and dispatching alerts to Slack, Microsoft Teams, Jira, ServiceNow, Tines, or a custom HTTP endpoint.
Which SaaS vendors and integrations are supported?
First-party remediation currently supports Microsoft and Google Workspace file and folder findings. Webhook actions support Slack, Microsoft Teams, Jira, ServiceNow, Tines, or any custom HTTP endpoint. Cloudflare says custom findings support is upcoming.
What is the five-minute remediation target for SaaS security?
Cloudflare targets detection to completed remediation in five minutes or less. This benchmark helps teams measure manual response workflows against automated, event-driven enforcement.
What logs do Cloudflare CASB policies generate?
Each policy action produces Admin Activity logs and Cloud and SaaS Security policies logs. Admin logs track who created, edited, or disabled a policy. Runtime logs capture the triggering finding, affected file, action taken, success or failure, and timestamp.
How do CASB policies handle approved exceptions for public file shares?
Admins can allow approved exceptions, such as marketing teams collaborating externally, while automatically revoking public access for shares outside the exception. This keeps the finding backlog clean and reduces the exposure window.